Did you know? · No. 17 · Status Is UP data ·
Fewer than 1 in 3 popular homepages we checked send a Content Security Policy
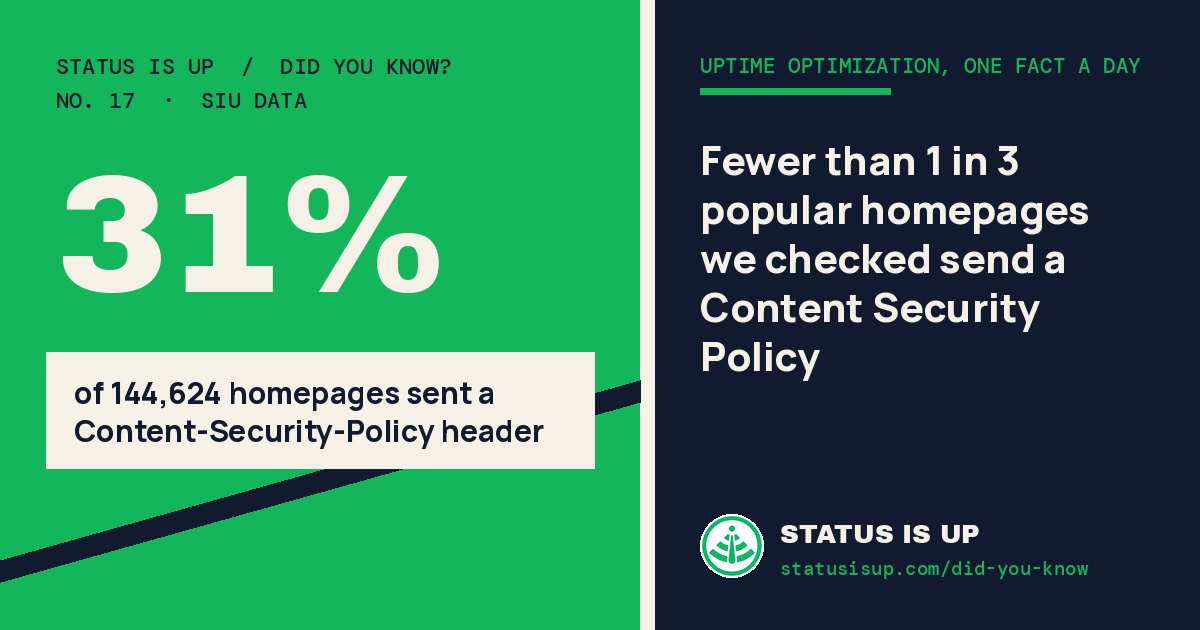
In Status Is UP’s October 2026 readiness snapshot, 31% of 144,624 measured homepages sent a Content-Security-Policy header. Among the top 1,000 sites in the Chrome UX Report list, it was 44%.
A Content Security Policy tells the browser where a page may load scripts, styles, frames and other resources from, which helps limit the damage of cross-site scripting and unwanted framing. It does not have to start strict. A small policy such as frame-ancestors 'self'; base-uri 'self'; object-src 'none' restricts who may frame your pages, blocks <base> tag injection and disables plugins, without touching analytics or ad scripts. Status Is UP sends that baseline itself.
To try a stricter script policy safely, send it in the Content-Security-Policy-Report-Only header first: the browser reports violations without blocking anything, so you can see what would break before you enforce it.
Try this on your site
Add the baseline header—frame-ancestors 'self'; base-uri 'self'; object-src 'none'—and confirm your pages, analytics and embeds still work. Then trial a stricter script policy with Content-Security-Policy-Report-Only before enforcing it.
Share this fact
Each fact is checked against the primary sources listed. Spotted an error? Email the Status Is UP team. Status Is UP helps owners improve their sites; it is not an uptime monitor. For live outage status, see Status Is Down.