
STATUS IS UPWEBSITE OPTIMIZATION WIKI
23Harden
Performance and delivery / Harden

Control Third-Party Scripts Before They Control Your Page

A practical system for finding outside scripts, proving value, loading safely, respecting consent, testing failure, and removing unused vendors.

Control Third-Party Scripts Before They Control Your Page — VISUAL GUIDE
READ
8 minutes
SOURCES
7
REVALIDATE
2027-03-27
reviewed
Performance engineering lead with privacy and application-security review for consent-gated or security-sensitive integrations
THE SHORT ANSWER

Start with the decision.

Treat every third-party script as a dependency with an owner, benefit, budget, consent category, and review date. Build one inventory from browser traces, tag manager, CMS plug-ins, and code. Record vendor domains, trigger, data exposed, and what breaks if the vendor is slow or absent. Remove duplicates and unowned tags first.

Keep nonessential code off the critical rendering path, the browser work needed to show the first screen. Load only code needed for the first task; delay independent widgets until interaction while preserving dependency order. Test priority journeys with consent accepted and refused and with vendor domains blocked. Code that cannot fail safely needs a fallback, isolation, or a different implementation.

VISUAL GUIDE

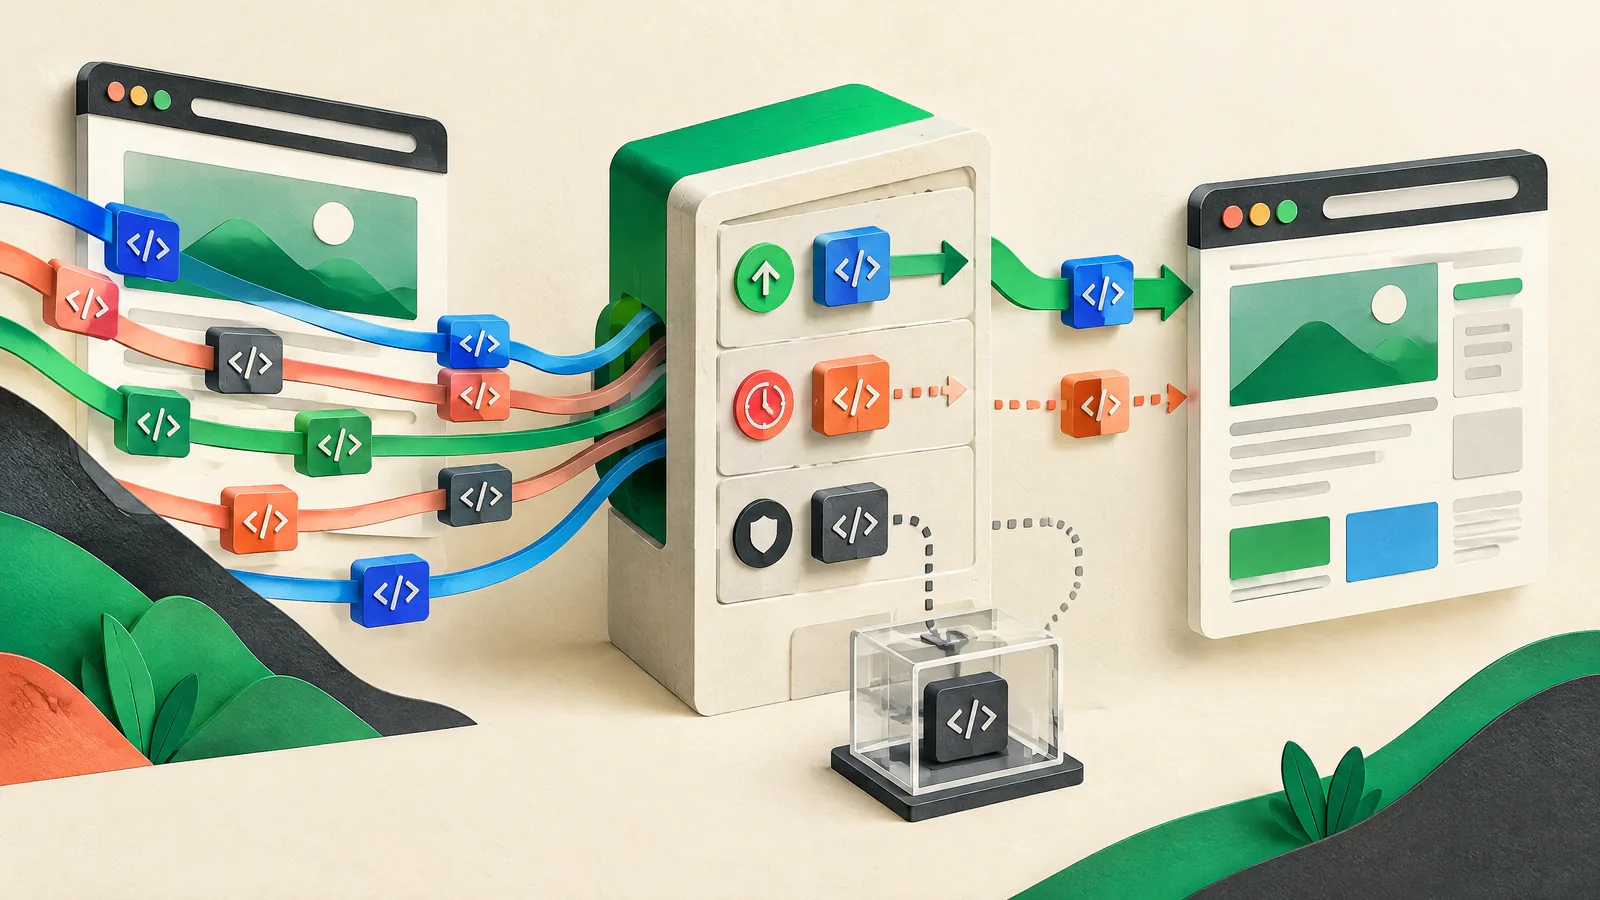
See the work as a system.

Use this map to connect the article’s decisions before acting on individual tactics.

SIUHarden
01Build one inventory from what the browser loads
02Make keep, remove, and budget decisions visible
03Load late only when late is safe
04Make consent the gate, not an afterthought
01

Build one inventory from what the browser loads

Start with representative pages: home, landing, detail, search, cart, checkout, account, and campaigns. Record fresh and return visits in Chrome DevTools. Compare browser evidence with tag manager, CMS plug-ins, and code dependencies; one view can miss injected scripts.

Use one row per vendor or integration, not just per URL. Capture domains it contacts and whether it can add tags. Give it a business owner who can defend the purpose and approve removal. Recheck after campaigns, vendor changes, template releases, and redesigns.

Minimum evidence

Save page, journey, vendor domains, requests, transfer size, main-thread work, and test conditions. A lab trace is diagnostic evidence, not a promise for every visitor.

Record the decision

Include purpose, owner, consent category, trigger, data exposed, dependency order, fallback, and review date.

02

Make keep, remove, and budget decisions visible

Ask each owner what would be worse if the integration disappeared. If vague, disable or remove it. web.dev recommends budgets, avoiding duplicate functions, and cleaning redundant scripts.

A budget is a team guardrail, not a universal threshold. Set per-vendor and page allowances for bytes, requests, main-thread time, and load timing. Compare the baseline with a change. Require the owner to stay within the allowance, remove another cost, or obtain an expiring exception. Use comparable journeys and user-centered metrics.

Keep

Keep only dependencies with a current purpose, owner-accepted cost and data use, and an acceptable failure path.

Remove

Retire expired pixels, duplicate analytics, inactive chat, unused experiments, and abandoned plug-ins through a staged release.

Exception

Record reason, cost, approver, compensating action, and review date.

03

Load late only when late is safe

Choose loading behavior deliberately. A classic external script without async, defer, or module behavior is fetched and executed before HTML parsing continues. With async, download runs in parallel but execution starts when ready, so order is not guaranteed. With defer, classic external scripts run after parsing and in document order, before DOMContentLoaded. Defer suits ordered scripts; it is not universal.

For optional chat, social, map, video, or recommendation interfaces, render a lightweight placeholder and load the vendor after a click or when relevant. This facade pattern starts with your control rather than the full embed. Preserve keyboard interaction and reserve space. Do not defer code required to calculate price, sign in, process payment, provide essential accessibility, or meet a confirmed obligation without a reviewed alternative.

Pick the trigger

Load immediately only for the first-task dependency; use post-parse for ordered code and interaction or visibility for optional embeds.

Respect order

Do not mark interdependent scripts async and expect order to hold. Document and test the published chain.

Avoid window load

Do not tie critical UI to window load; third-party embeds can delay it even when async or defer is used.

04

Make consent the gate, not an afterthought

Classify each vendor with privacy and legal stakeholders who understand jurisdictions and data flows. For a consent-gated integration, establish consent state before the tag sends relevant data. Google says its default consent command should run before measurement commands, and updates should follow a changed choice. This product guidance is not legal advice.

Test first visit with no choice, acceptance, refusal, and withdrawal. Check the interface and network: a hidden widget does not prove no request or identifier was sent. If the consent platform loads asynchronously, test timing. Persist choices appropriately and apply changes on the current page and later visits.

Document classification

Do not rely on a vendor label. Record why the tag is essential, optional, or prohibited for a region or journey and obtain approval.

Verify withdrawal

After withdrawal, confirm configured nonessential tags do not load or send data and keep test evidence.

05

Reduce the blast radius of code you do not control

OWASP identifies loss of control over client changes, arbitrary code execution in browsers, and sensitive-data disclosure as central risks. Limit tag-publishing access, review custom HTML or arbitrary-code features, and document allowed data-layer fields. Vendor agreements and qualified security review can help for high-risk integrations; neither replaces testing.

Subresource Integrity, or SRI, lets a browser verify a script against a cryptographic hash. It helps only when a resource can be pinned and cross-origin delivery supports CORS; W3C says using SRI without CORS is a logical error. It is a poor fit for many changing vendor URLs. An iframe sandbox may reduce direct access to the host DOM and cookies, but needs specialist review. Payment and security-sensitive flows merit qualified review.

Minimize data

Pass only documented fields needed for the purpose. Do not expose secrets, payment data, or unnecessary customer attributes.

Know the limit

SRI verifies bytes, not whether data use or later requests are appropriate; isolation is not a drop-in fix.

06

Practice vendor failure before customers encounter it

For each retained vendor, block its domains in a test environment or browser request blocker, then exercise the journey. Also test slow responses and a tag-manager configuration without the integration. Confirm primary content, navigation, forms, checkout, and account access behave as intended. This exposes assumptions before release.

Define remediation before an incident: who can disable the tag, whether a flag or tag-manager publish is required, how to roll back, and how to verify. SIU is proactive uptime optimization and remediation: use inventory, budgets, preflight, and rollback practice to reduce dependency risk. SIU cannot control vendor infrastructure, guarantee availability, or replace review.

Set success criteria

State what remains usable without the vendor, what may degrade, the fallback, and the maximum delay before disablement.

Keep release proof

Attach a before-and-after trace, consent result, blocked-vendor result, and rollback owner to the change record.

ACTION / VERIFY

Your practical to-do guide.

  1. 01

    Capture the dependency set

    Trace priority templates, then compare browser evidence with tag-manager, CMS, and code inventories.

    VERIFY: Every third-party domain links to an inventory row or is investigated before release.
  2. 02

    Assign the owner

    Name the person accountable for purpose, cost, data use, and renewal.

    VERIFY: No retained integration lacks an owner, purpose, or review date.
  3. 03

    Remove redundant code

    Stage removal of duplicate analytics, expired pixels, dormant experiments, and unused plug-ins.

    VERIFY: Required journeys and reporting are checked after removal.
  4. 04

    Set budgets

    Set page and vendor allowances for requests, bytes, main-thread work, and timing.

    VERIFY: The release record compares the change with the allowance and records any expiring exception.
  5. 05

    Validate loading and consent

    Test dependency order, fallback, keyboard use, and consent choices.

    VERIFY: Network inspection matches approved loading and consent behavior.
  6. 06

    Review boundaries

    Limit publishing access, document data fields, and assess SRI or isolation only where their constraints fit.

    VERIFY: The integration has appropriate security or privacy review for its risk.
  7. 07

    Block the vendor

    Simulate an unavailable or slow vendor and run the essential journey end to end.

    VERIFY: Critical tasks meet fallback criteria, or the risk is redesigned or explicitly accepted.
  8. 08

    Rehearse disable and rollback

    Document the authorized disable route and return to the known-good configuration.

    VERIFY: A named person has tested the steps in nonproduction and recorded the result.
DISCUSSION TOPICS

Compare the trade-offs, not private data.

Use these prompts with your team or website-owner community. Share methods and lessons, but never paste credentials, customer records, or non-public infrastructure details.

  1. 01

    Which third-party integration on your site has the clearest measurable benefit, and what evidence made that decision easy?

  2. 02

    What fallback kept a customer journey useful when an optional widget, embed, or measurement vendor was unavailable?

  3. 03

    How do your product, marketing, privacy, and engineering teams decide when a temporary tag exception should expire?

POPULAR / AUTHORITATIVE RESOURCES

Open the source material.

web.devLoad Third-Party JavaScript ↗

Google guidance for finding costly resources, measuring impact, delaying loading, and self-hosting.

Reviewed 2026-09-27
web.devThird-party JavaScript performance ↗

Overview of third-party network and rendering costs, budgets, and cleanup.

Reviewed 2026-09-27
MDN Web Docsscript: The Script element ↗

Reference for classic scripts, async, defer, modules, integrity, and errors.

Reviewed 2026-09-27
OWASPThird Party JavaScript Management Cheat Sheet ↗

Security guidance on third-party risks, tag controls, sandboxing, integrity, and data exposure.

Reviewed 2026-09-27
Google for DevelopersSet up consent mode on websites ↗

Official Google-tag guidance for consent defaults, updates, timing, and persistence.

Reviewed 2026-09-27
W3CSubresource Integrity ↗

Specification for script integrity metadata and cross-origin constraints.

Reviewed 2026-09-27
Chrome for DevelopersPerformance features reference ↗

How to record traces and distinguish first- and third-party events.

Reviewed 2026-09-27

Source policy. This article uses directly read public primary or authoritative documentation. Resources are selected for implementation details, not snippets. Product documentation does not determine legal obligations. Internal and SID links are navigation, not evidence.

QUICK CLARIFICATIONS

Common questions.

Should every third-party script use async?

No. Async removes parser blocking during download but does not guarantee order and can interrupt rendering. Use it for independent scripts; use defer for ordered classic scripts, and interaction triggers for optional embeds.

Can we self-host vendor JavaScript to make it reliable?

Not automatically. It can increase control over caching and delivery, but makes you responsible for compatibility and security updates. Confirm vendor terms, patching ownership, and regression testing first.

Does SRI make a vendor script safe?

No. SRI can verify expected bytes when delivery supports it. It does not assess intended behavior, data collection, or later network activity, and is impractical for many changing scripts.

Status Is UP Editorial Team · Uptime Enablement Editors

Reviewed by Performance engineering lead with privacy and application-security review for consent-gated or security-sensitive integrations. Published 2026-09-27; updated 2026-09-30.